

AI Security Posture Management
Your Agents Are Shipping. Is Your Security Keeping Up?
Trent helps you find, prioritize, and fix the risks your agentic systems introduce before they become production problems.

The gap
Your AI Security Posture Has a Blind Spot
AI agents expand your attack surface faster than traditional security tools can adapt. New behavior, new tools, and constant iteration create risk your current stack was not built to see.
Your Scanners Miss What Agents Introduce
Traditional security tools find code-level vulnerabilities. They can’t reason about agent behavior, multi-step autonomy, or the new threat surfaces created when AI agents call APIs, chain tools, and act on behalf of users.
New Threat Surfaces Your Tools Were Never Designed to See
A single AI agent can access external data, call third-party services, modify databases, and trigger downstream agents from a single prompt. Prompt injection, tool misuse, unintended autonomous actions, data exfiltration through agent chains, privilege escalation across interconnected agents. Traditional scanners, firewalls, and SAST/DAST tools are blind to all of it.
Point-in-Time Audits Are Already Outdated
Agentic systems don’t ship in releases. They run, learn, and adapt in real time. An agent’s behavior today may differ from its behavior tomorrow as models update, prompts change, and new tools are connected. Your AI security posture management needs to be continuous, not periodic.
How it works
Multiple Agents. One Continuous Loop. AI-SPM That Compounds.
Trent deploys specialized security agents that continuously scan, judge, mitigate, and evaluate your environment. Each cycle improves the next, so your security posture gets sharper as your systems evolve.
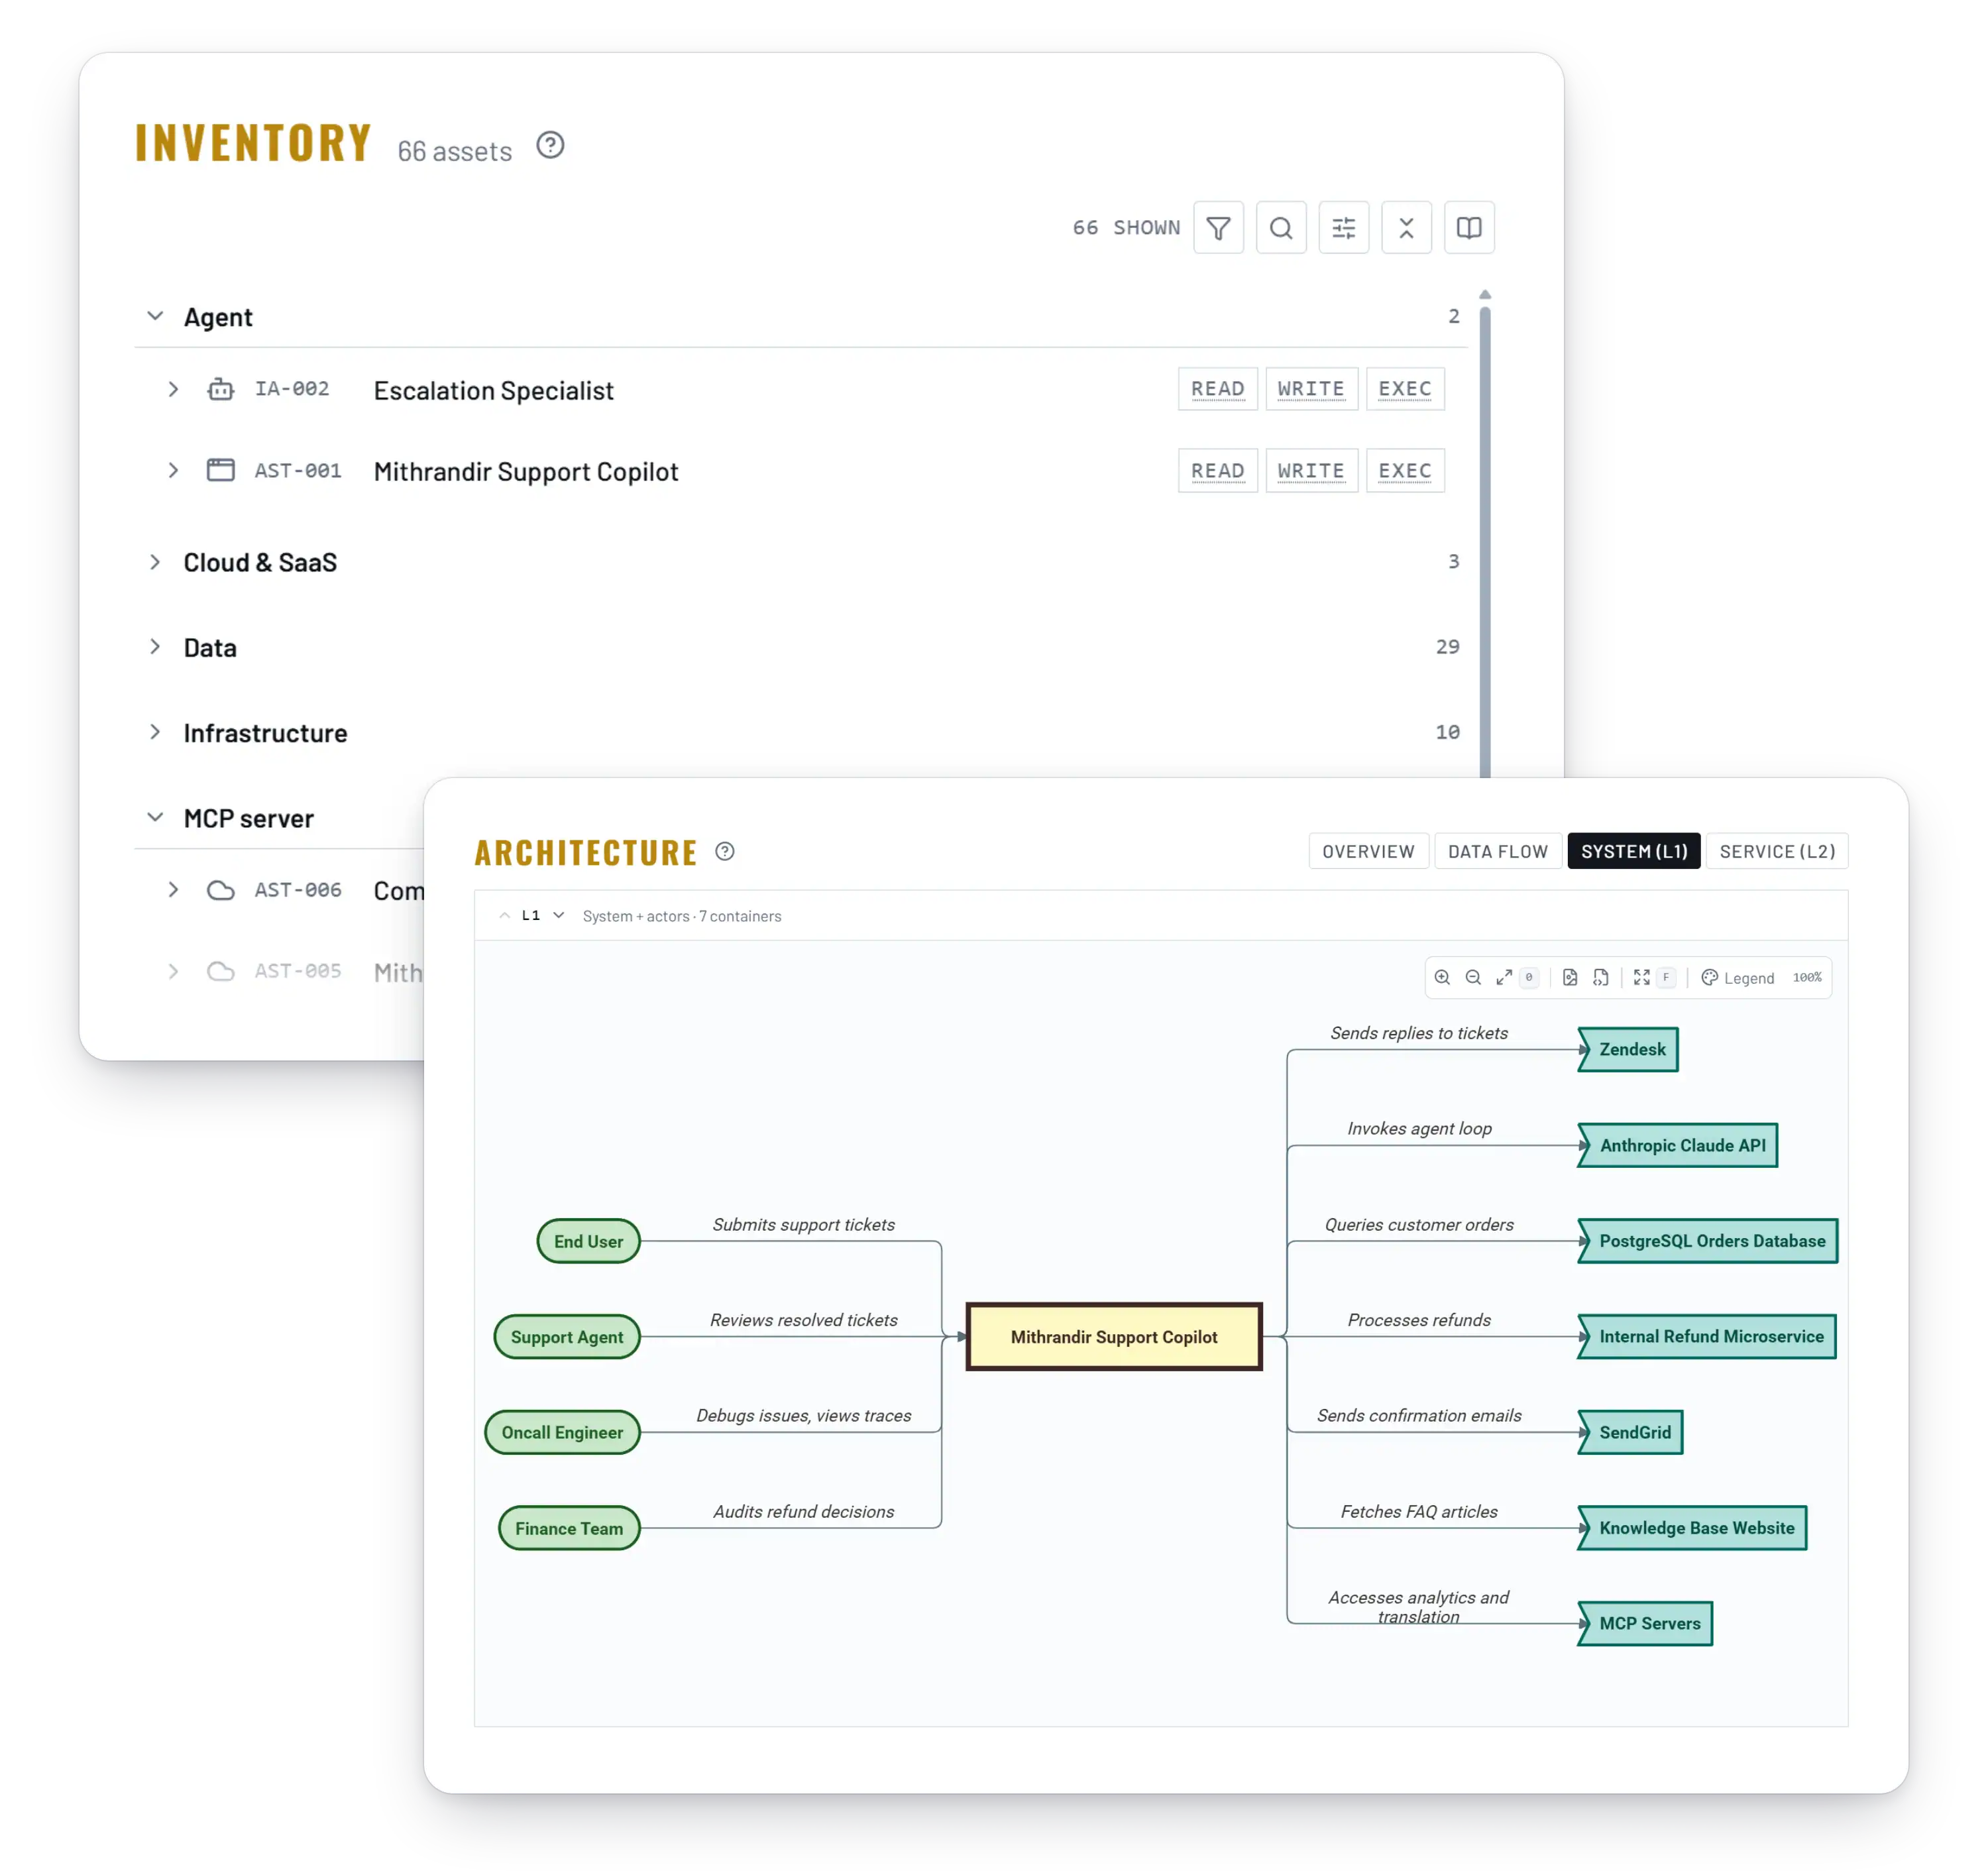
Scan
Continuously observe agents, code, infrastructure, and dependencies. They learn where to look for risks and what matters in each environment. Over time, Trent’s agents reduce noise, focus attention on high-risk surfaces, and flag increasingly high-signal observations.
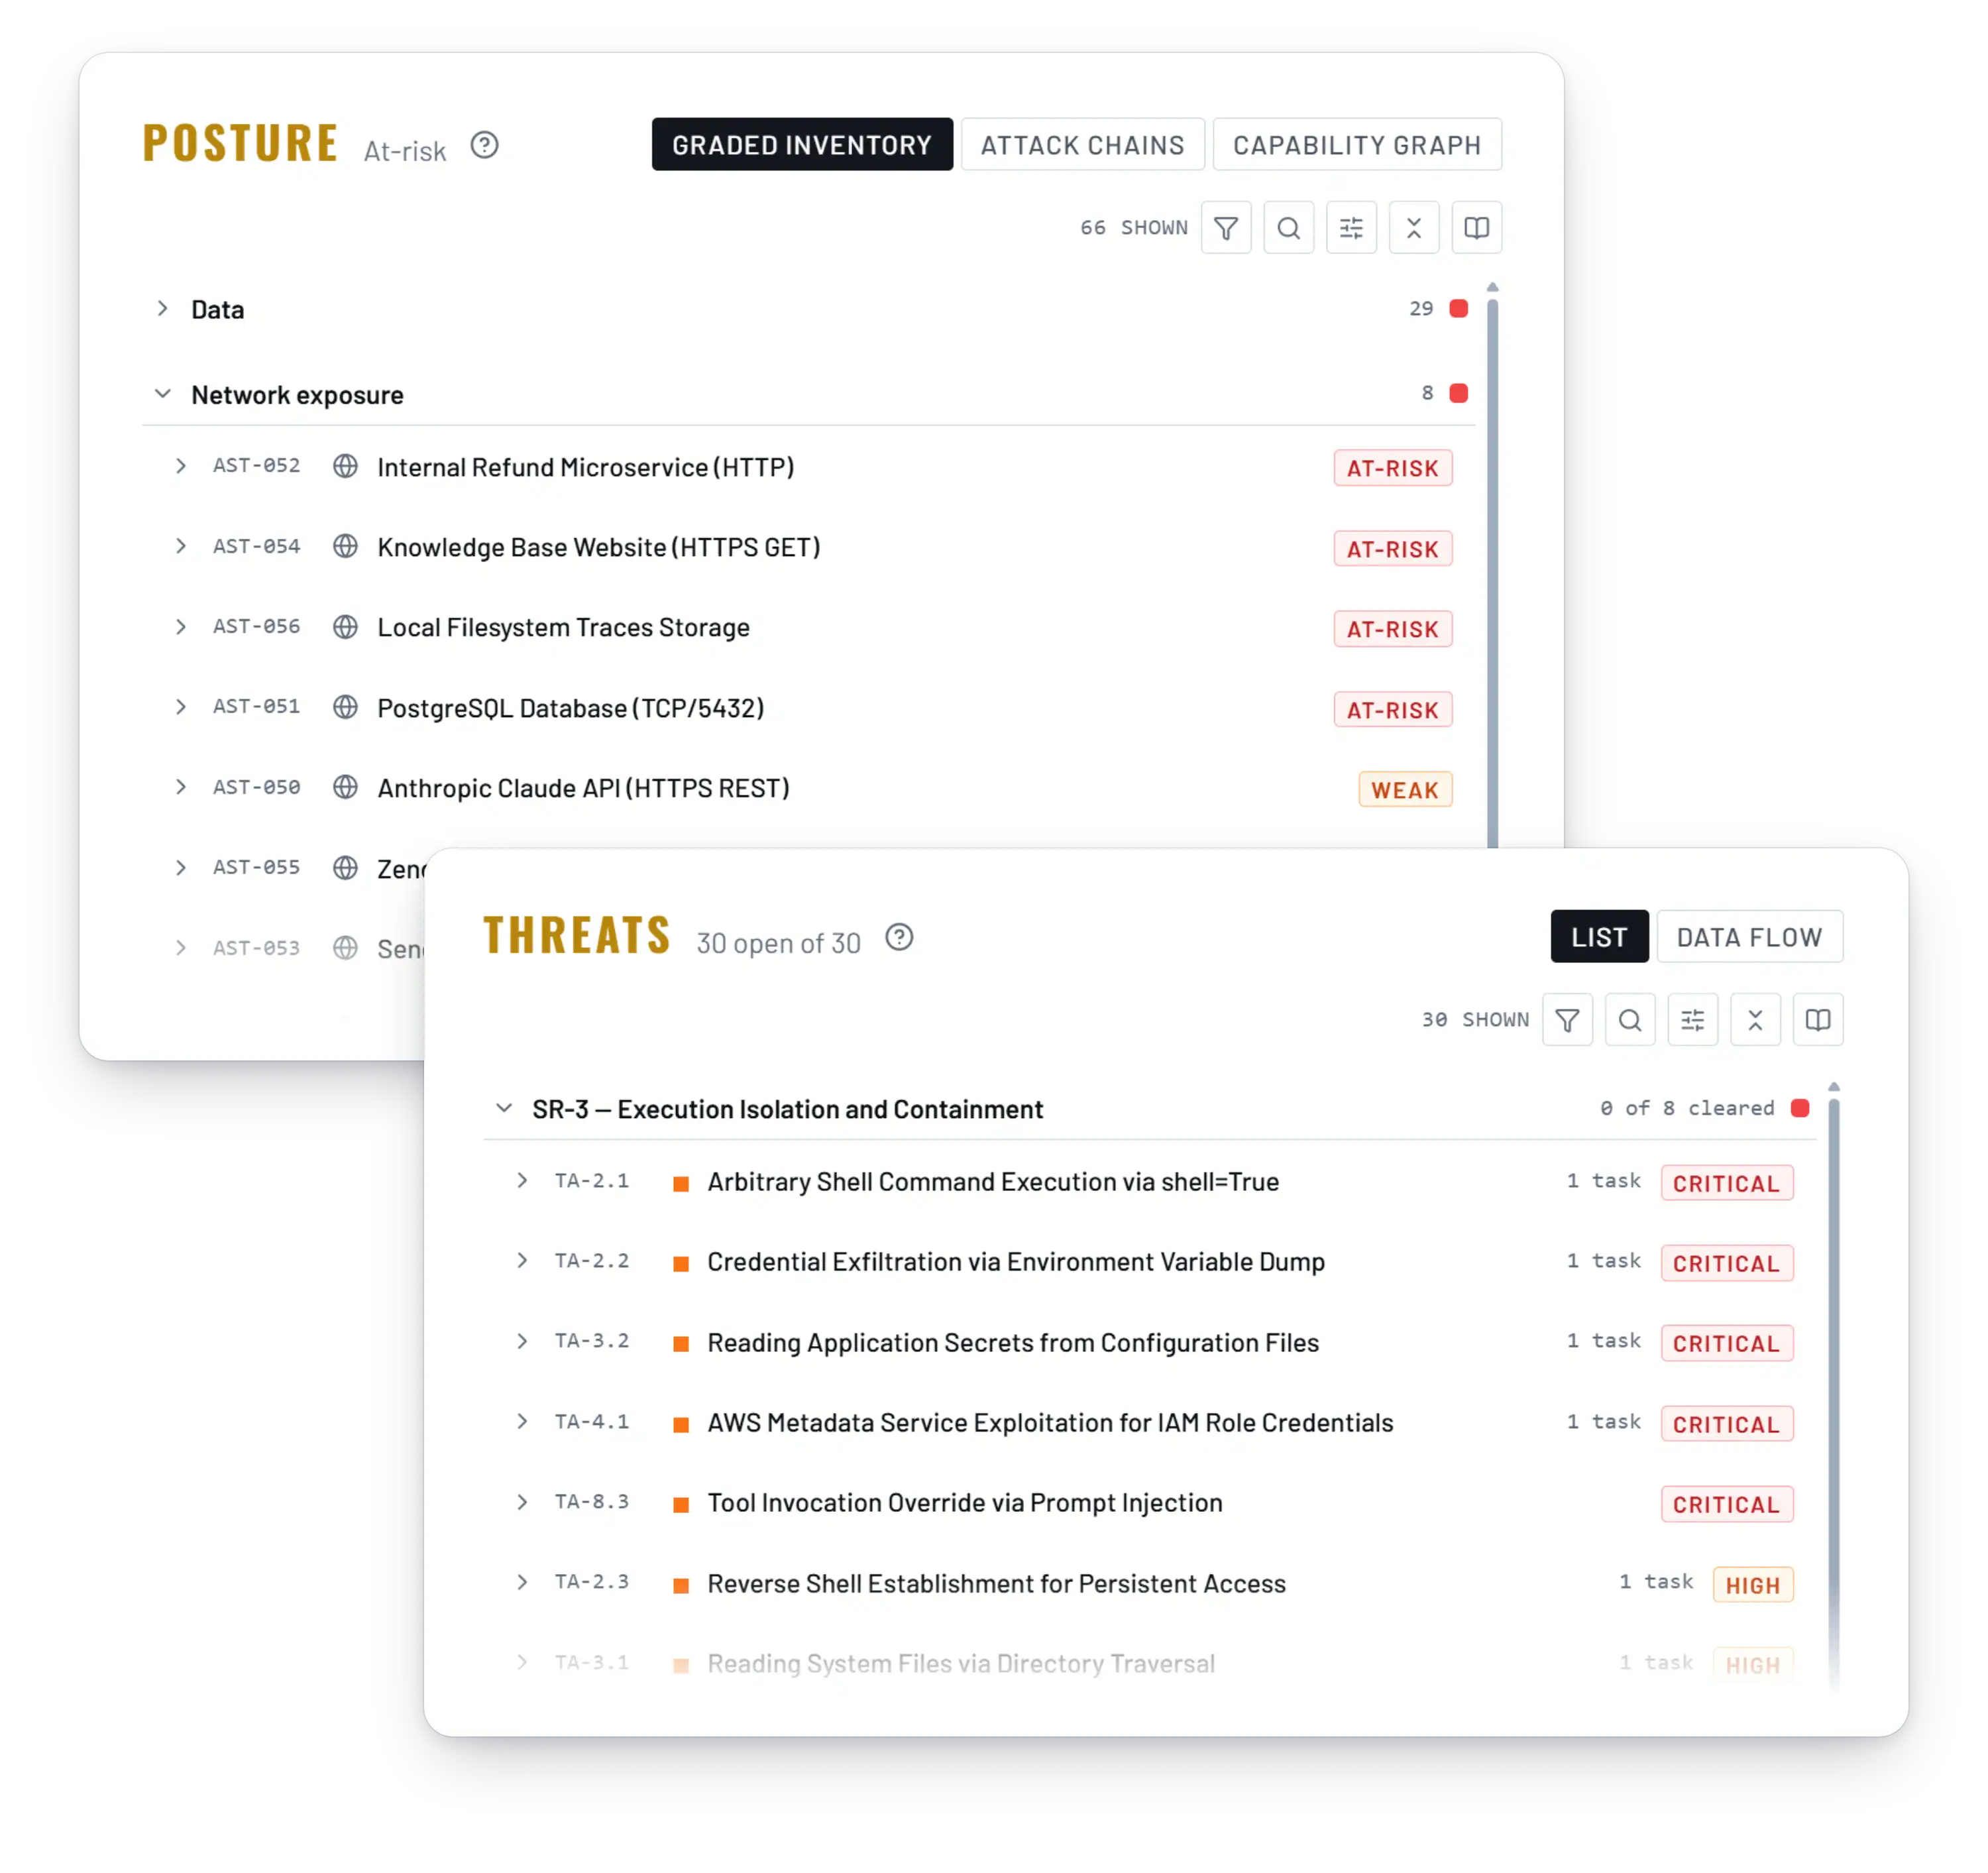
Judge
Take findings and determine what they mean. They classify signal vs. noise, assess business impact, and prioritize based on real risk rather than static rules. As they accumulate context across environments and historical outcomes, their judgments become sharper and more predictive.
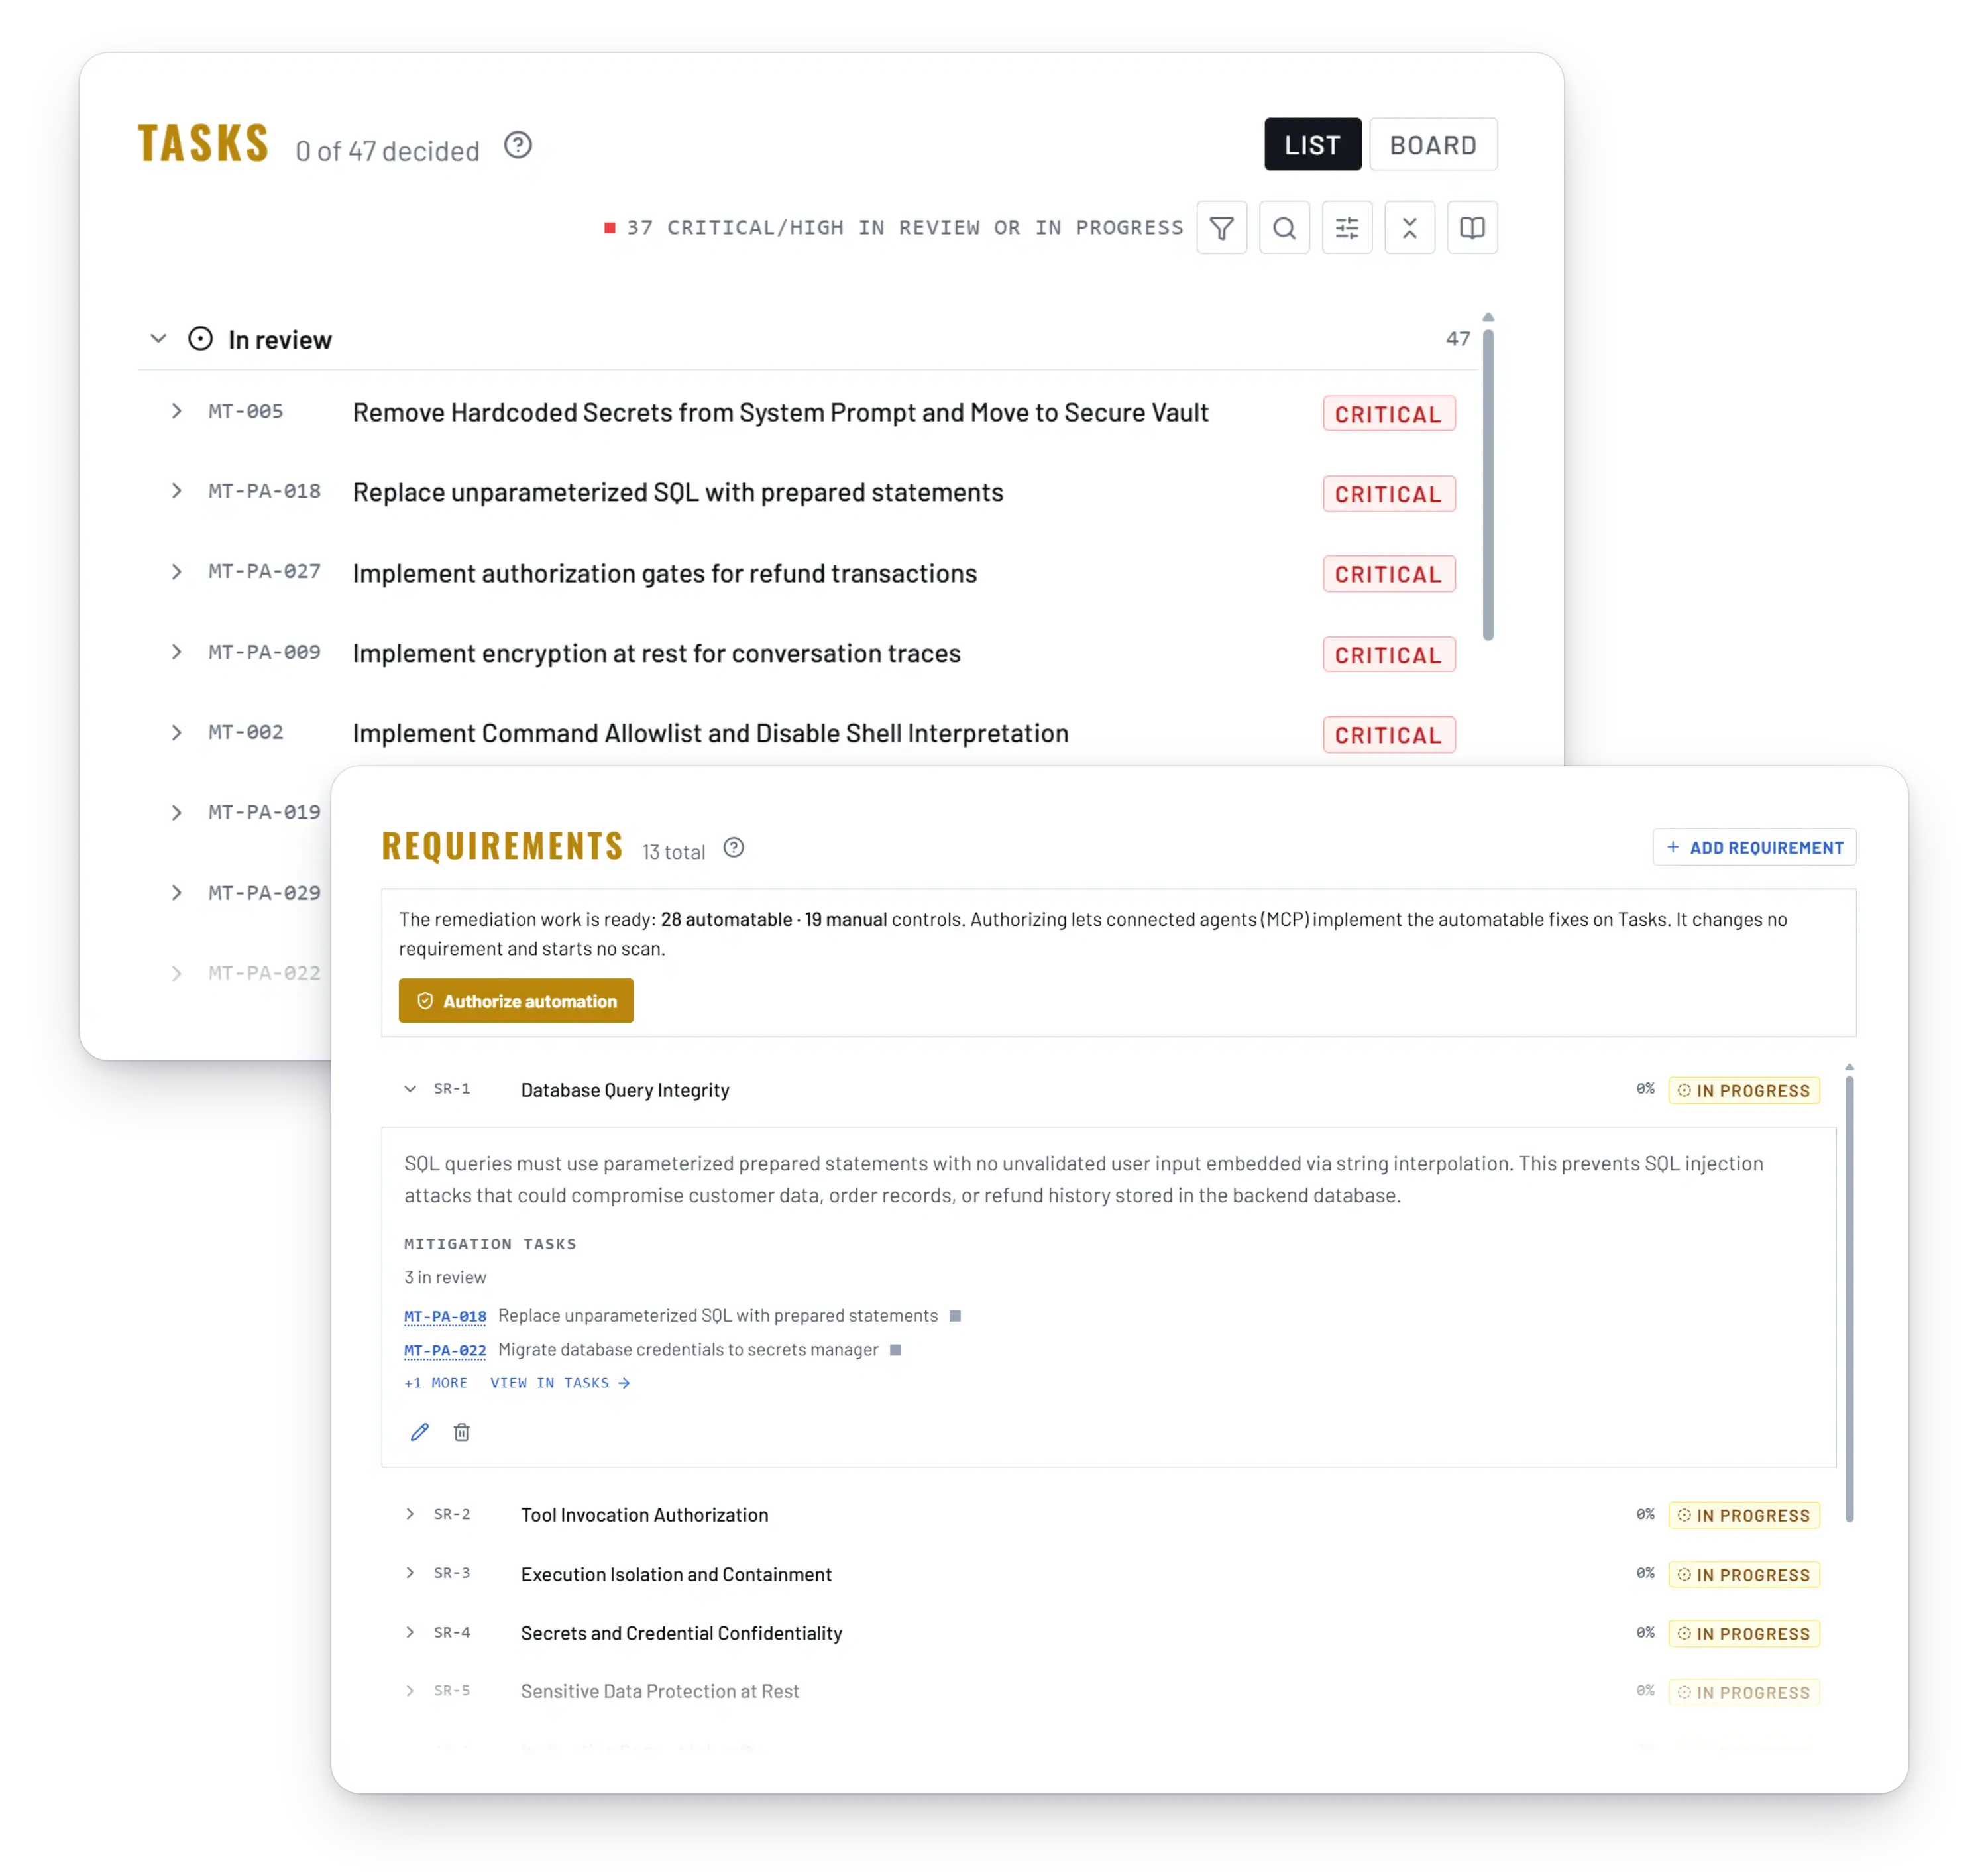
Mitigate
Agents act on prioritized risks. They patch vulnerabilities, open pull requests, adjust configurations, and validate that fixes actually work. Because they observe which remediations succeed, and which fail, they continuously improve their effectiveness within each customer’s stack.
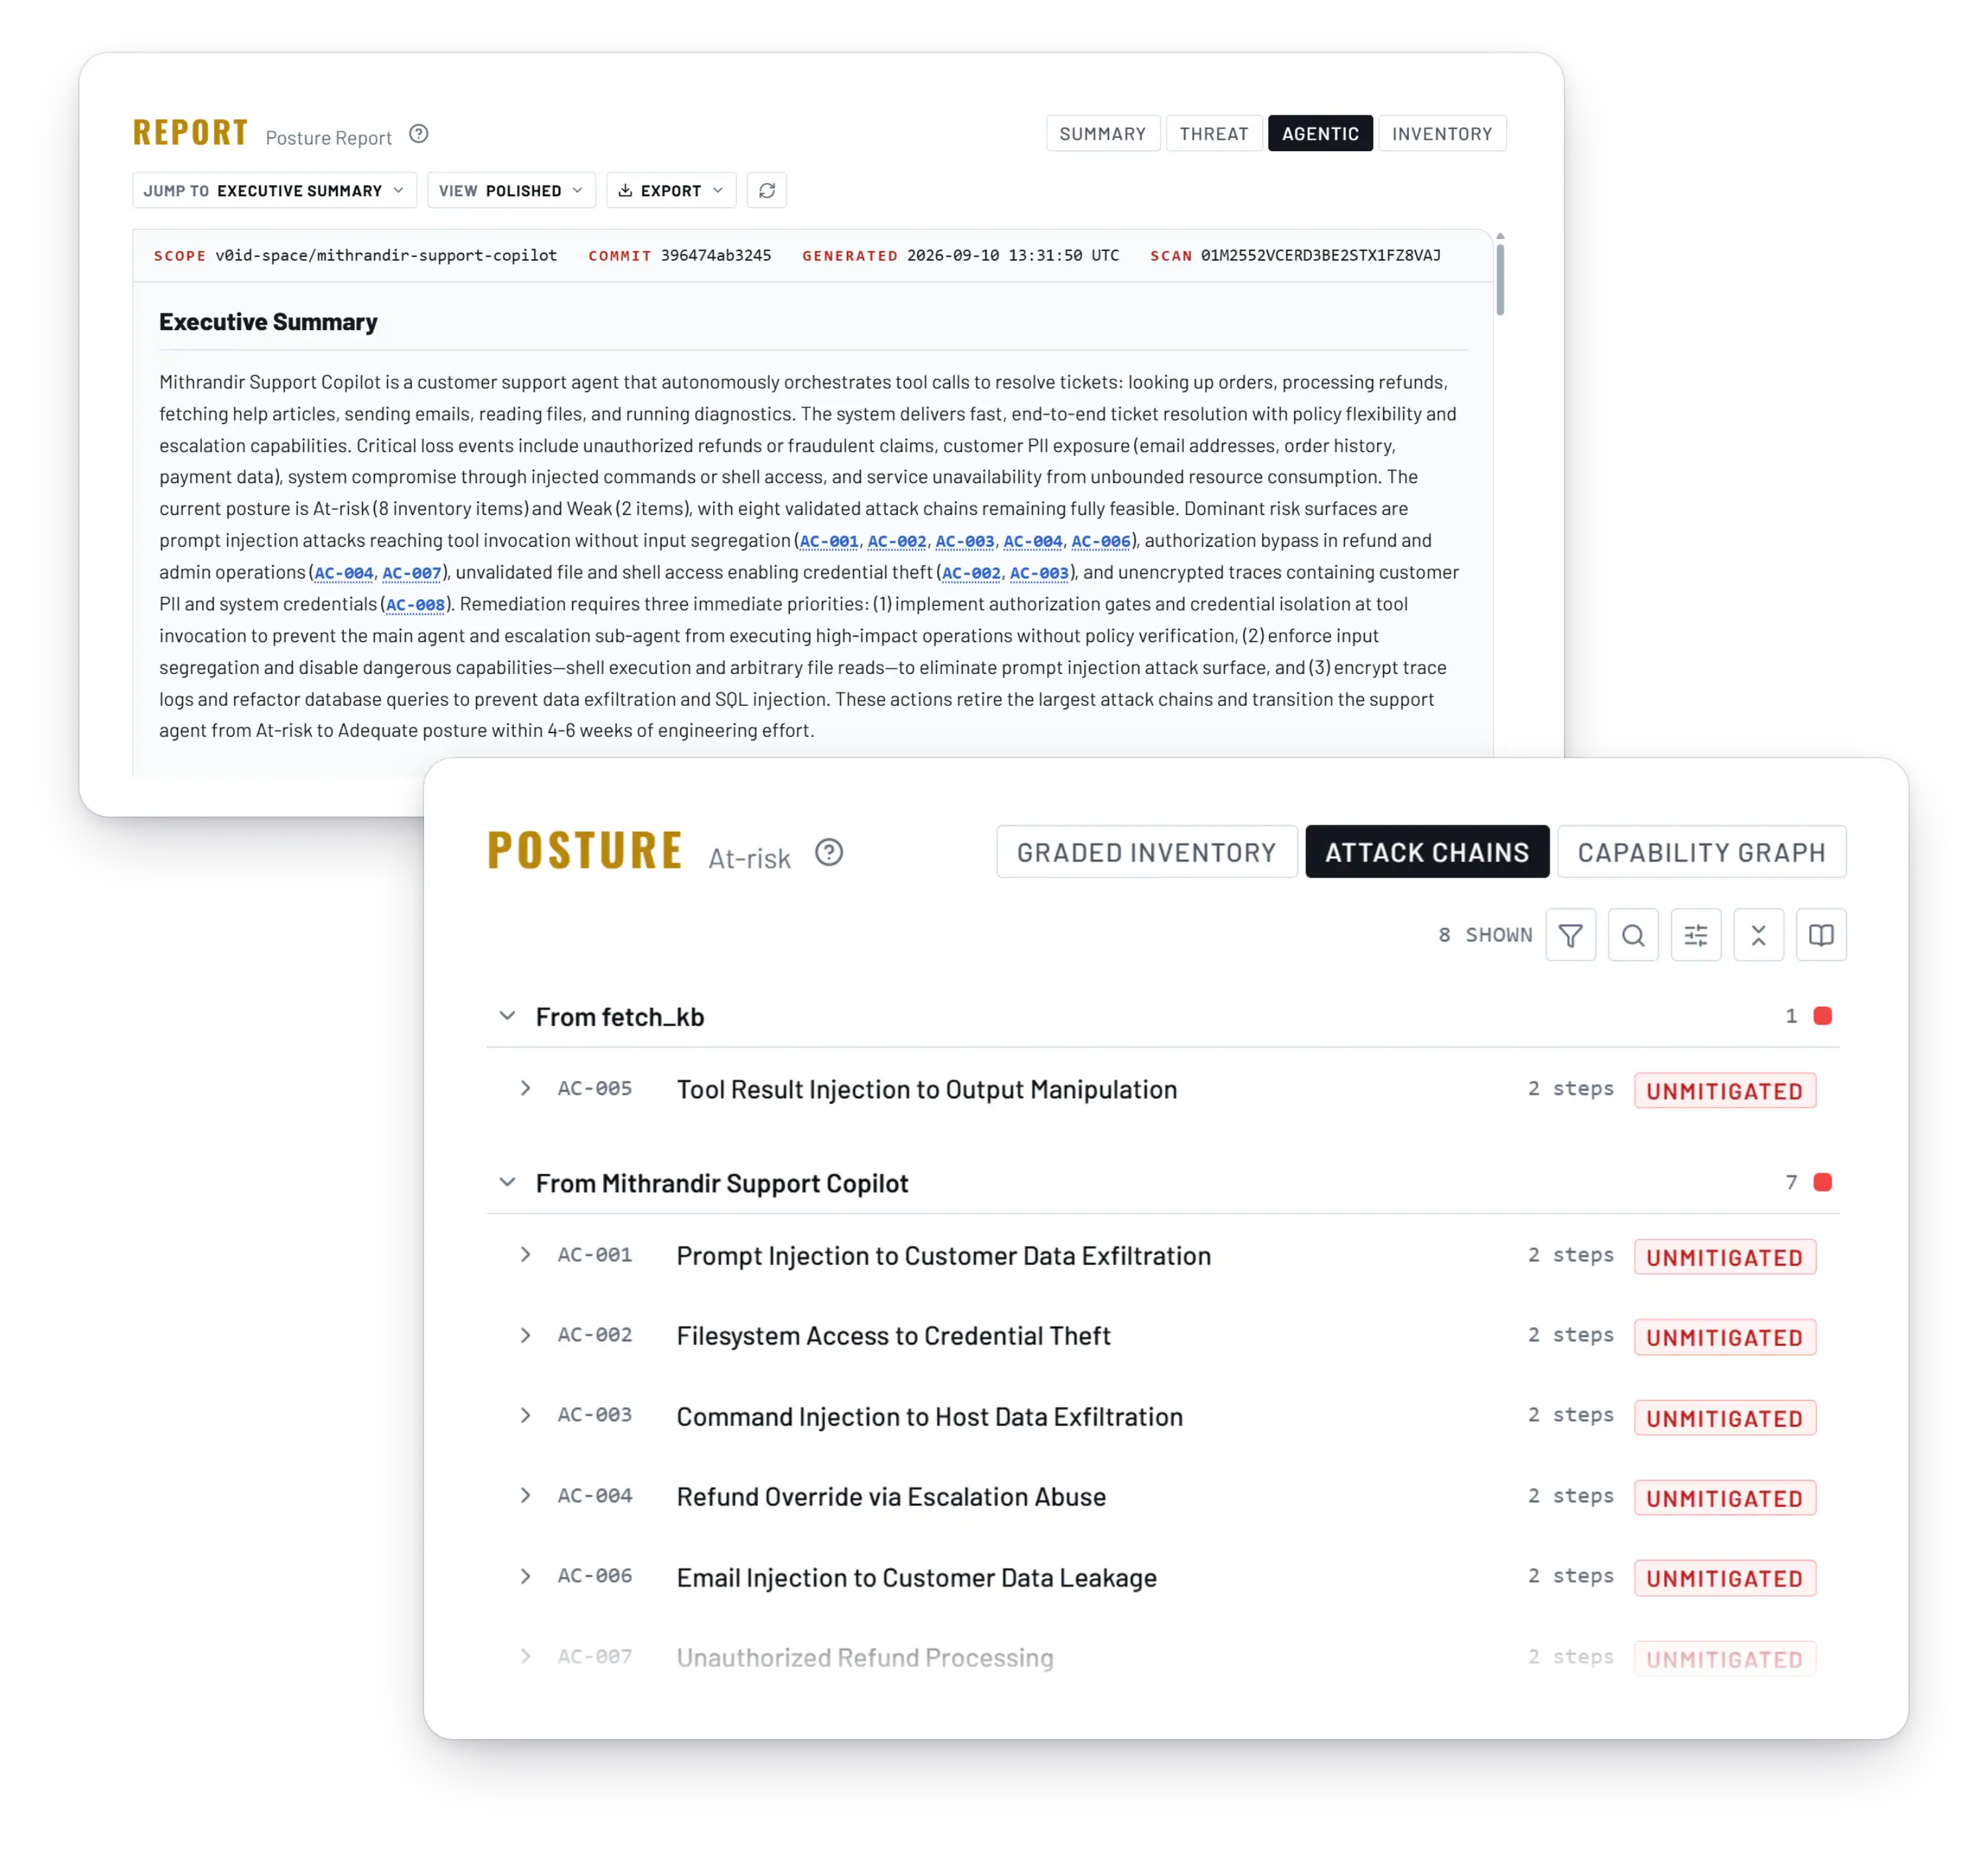
Evaluate
Step back and assess the system as a whole. They track trends, quantify risk over time, benchmark against standards, and identify systemic weaknesses. As the system compounds data, these agents become increasingly good at forecasting where risk will emerge next, informing smarter scanning and tighter prioritization.
Get started
Three Steps. No Configuration Overhead.
Connect
Connect your code, agents, or environment so Trent can understand how your system works.
Assess
Trent builds a prioritized, always-current security assessment grounded in your real architecture.
Evolve
Review the plan, execute fixes, and let Trent keep reassessing as your agents evolve.
Integrations
Works With Your AI Stack
- Claude Code
- Codex
- Cursor
- OpenClaw
- GitHub
Next step
Your Agents Don’t Stop Evolving. Neither Should Your Security.
Your AI application has risks your existing security stack was never designed to find.
FAQs
What is AI security posture management (AI-SPM)?
AI security posture management (AI-SPM) is the continuous process of discovering, grading and improving the security of AI systems: agents, LLM-powered applications and agentic workflows. Unlike traditional application security tools that focus on known code vulnerabilities, AI-SPM addresses the unique threat surfaces created when AI systems reason, act, and interact autonomously. It covers prompt injection risks, agent-to-agent privilege escalation, tool misuse, data exfiltration through agent chains, and configuration drift in agentic environments.
How is AI-SPM different from CSPM or DSPM?
Three posture tools, three different questions. CSPM asks whether your cloud is configured safely. DSPM asks where your sensitive data lives and who can reach it. AI-SPM asks what your AI agents can do and what happens when untrusted input steers them.
| Category | What it watches | Typical finding | Where Trent fits |
|---|---|---|---|
| CSPM (Cloud Security Posture Management) | Cloud infrastructure: storage, network rules, IAM roles, misconfigurations | A public S3 bucket, an open security group | Out of scope. Trent reads your code and configs, not your cloud account. |
| DSPM (Data Security Posture Management) | Sensitive data: where it is stored, who can access it, how it moves | Customer PII in an unencrypted store | Partly. Trent flags data stores your agents can reach and grades the exposure, but does not classify data at rest. |
| AI-SPM (AI Security Posture Management) | AI agents and LLM applications: tools, permissions, prompts, MCP servers, chained actions | An agent with a shell tool reachable from a customer message | Core. Trent inventories every agent, tool, skill and MCP server, grades each one, and traces the attack chains between them. |
How does Trent AI’s approach differ from traditional security scanners?
Traditional scanners (SAST, DAST, SCA) find known code-level vulnerabilities: CVEs, insecure dependencies, flagged patterns. They don’t assess whether your application is architecturally secure for what it does. Trent AI’s four specialized agents work in a continuous loop: scanning your environment, judging risk based on business context, remediating issues, and evaluating your overall posture. Each cycle compounds intelligence from the last, reducing false positives and sharpening prioritization over time.
Do I need to give Trent AI access to my source code?
You can start with a URL-only assessment that analyzes your application’s publicly visible attack surface, no code access required. For deeper analysis, connect a source code repository. Trent AI also accepts agent definitions, design documents, and product specifications to sharpen its assessment. You control what level of access to provide.
How do I get started?
Connect your source (repositories, agent definitions, or a URL), and Trent AI begins its first assessment cycle. You can add context like design docs, compliance requirements, technical constraints at any point.
What should an AI-SPM tool cover for AI agents?
Five things. If a tool cannot show you all five for your own agents, it is a cloud posture tool with an AI label.
- Inventory. Every agent, tool, skill, MCP server and data store in the codebase, found from the code and configs, not from a questionnaire.
- Permission grading. What each component can actually do: read, write, execute, reach the network. Graded so the risky ones stand out.
- Attack chain tracing. The paths where untrusted input meets the power to act, across components that each look fine alone.
- Remediation tracking. Findings as tasks with a concrete fix, a human approval step, and confirmation that the fix landed.
- Posture over time. A re-grade after every change, so you can see whether the last release made things better or worse.