The Two Cybersecurity Problems AI Leaders Need to Understand
AI speeds up attacks on familiar software flaws. AI agents can also act outside the authority you gave them. Why each problem needs a different response.
AI speeds up attacks on familiar software flaws. AI agents can also act outside the authority you gave them. Why each problem needs a different response.
73 posts
Follow the Winners (FTW), our NeurIPS 2026 paper: RL fine-tuning for LLM agents with no repeated attempts and no second model, just a buffer of winners.
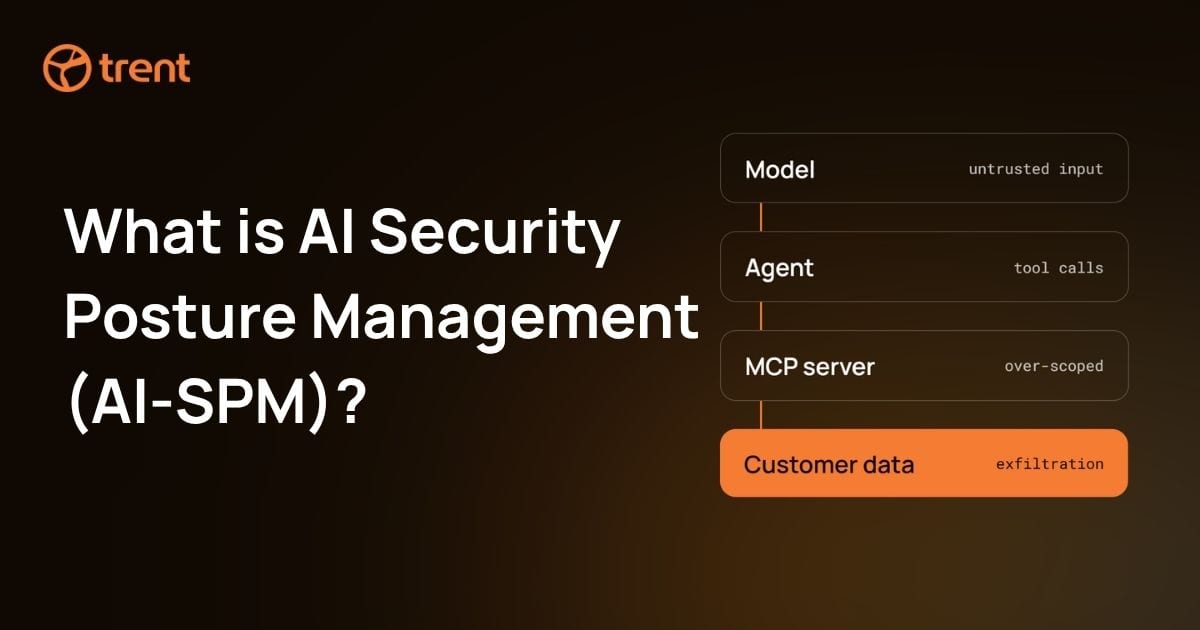
AI-SPM (AI security posture management) explained: what it covers, how it compares with CSPM, DSPM and ASPM, and the main AI-SPM vendors in 2026.
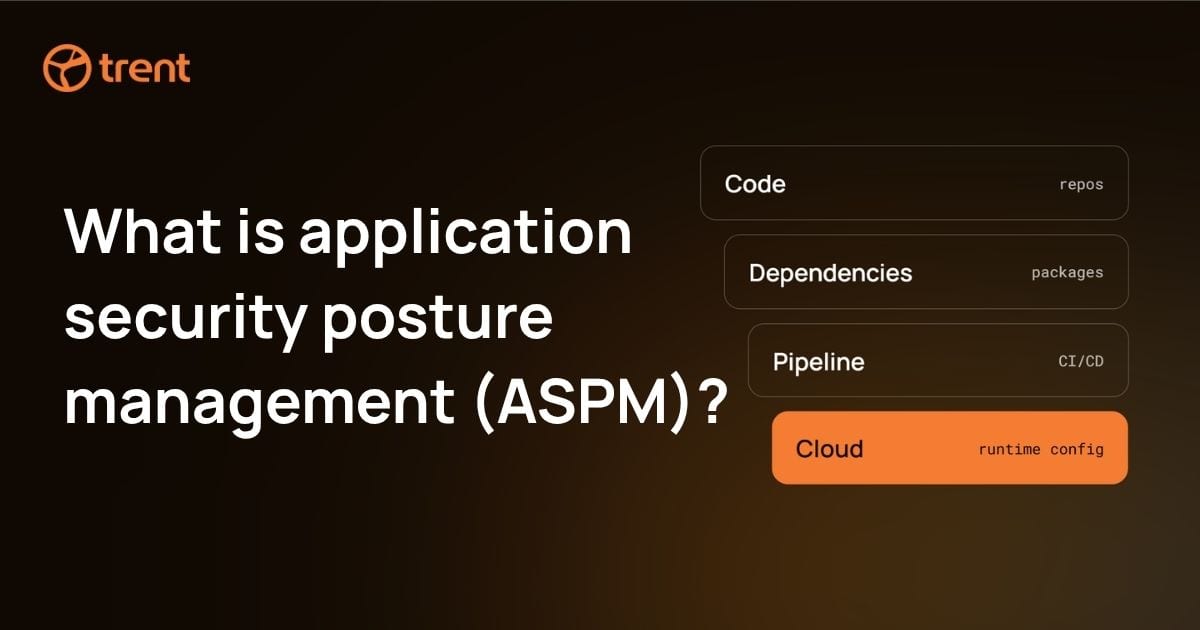
ASPM (application security posture management) explained: what it does and doesn't, how it compares with CSPM, CNAPP and AI-SPM, and when you need it.
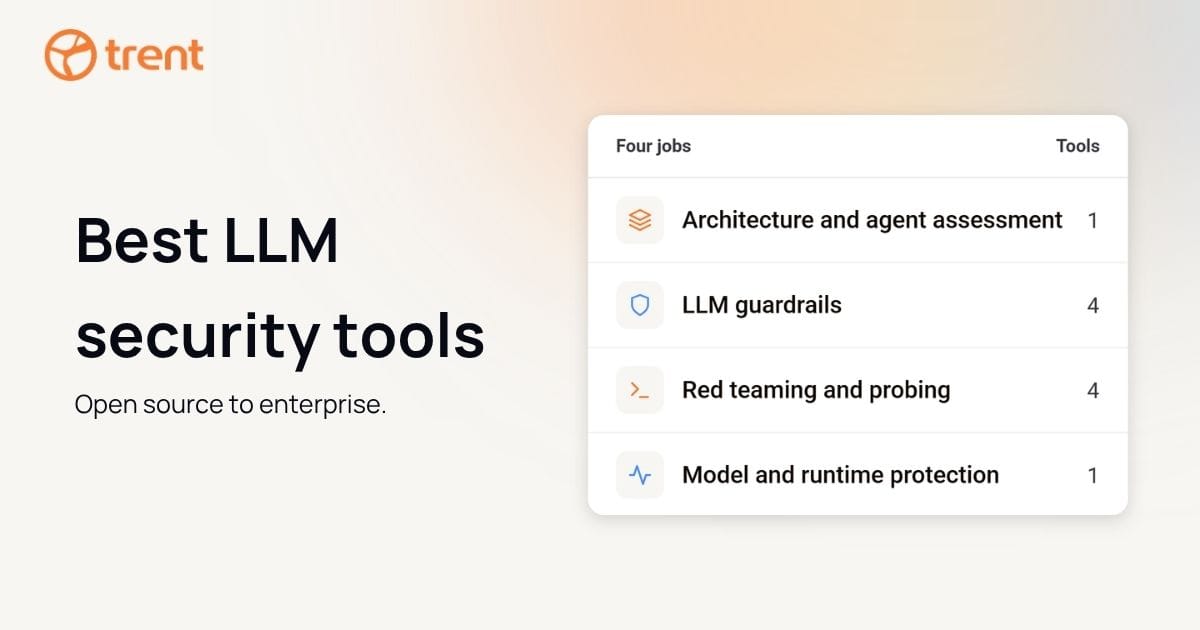
Compare 10 LLM security tools for 2026, from free open source scanners to enterprise guardrails. Pricing, deployment and what each one is best for.
Compare 16 AI security tools and platforms for 2026 by category: agent security, AI posture management, data protection, model supply chain and guardrails.
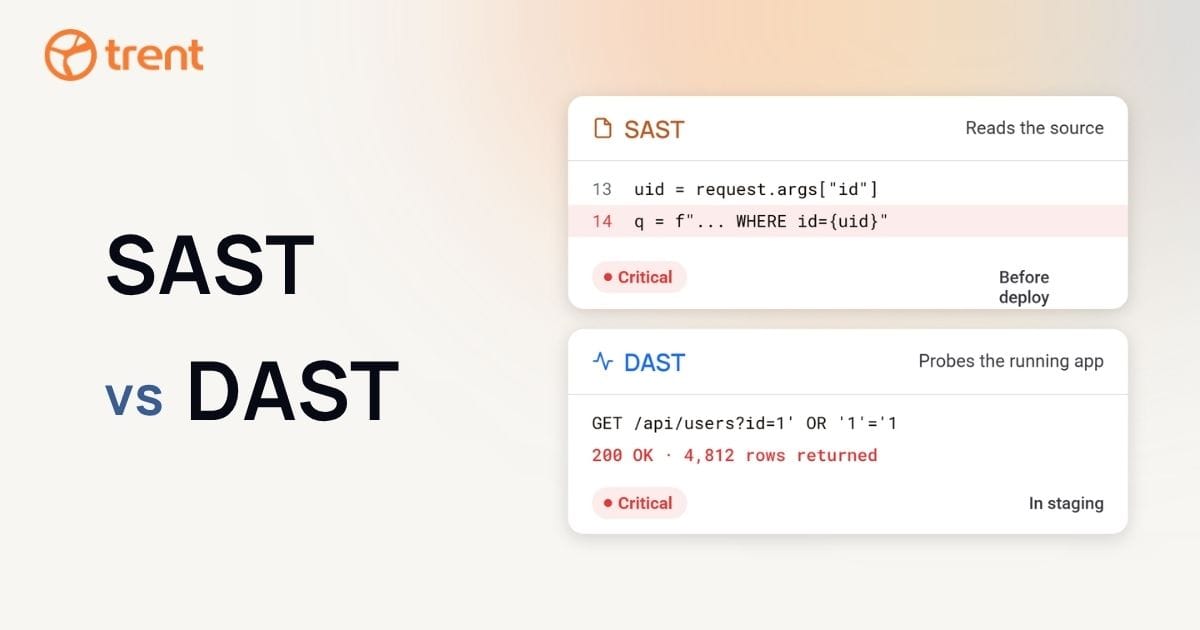
SAST vs DAST: what each finds, what each misses, and where SCA and AI-assisted review fit. A comparison table with named tools and real CVEs.
How Trent moved coding agents from a local MCP package to a hosted server and plugin, and what it taught us about when an agent should ask or act.
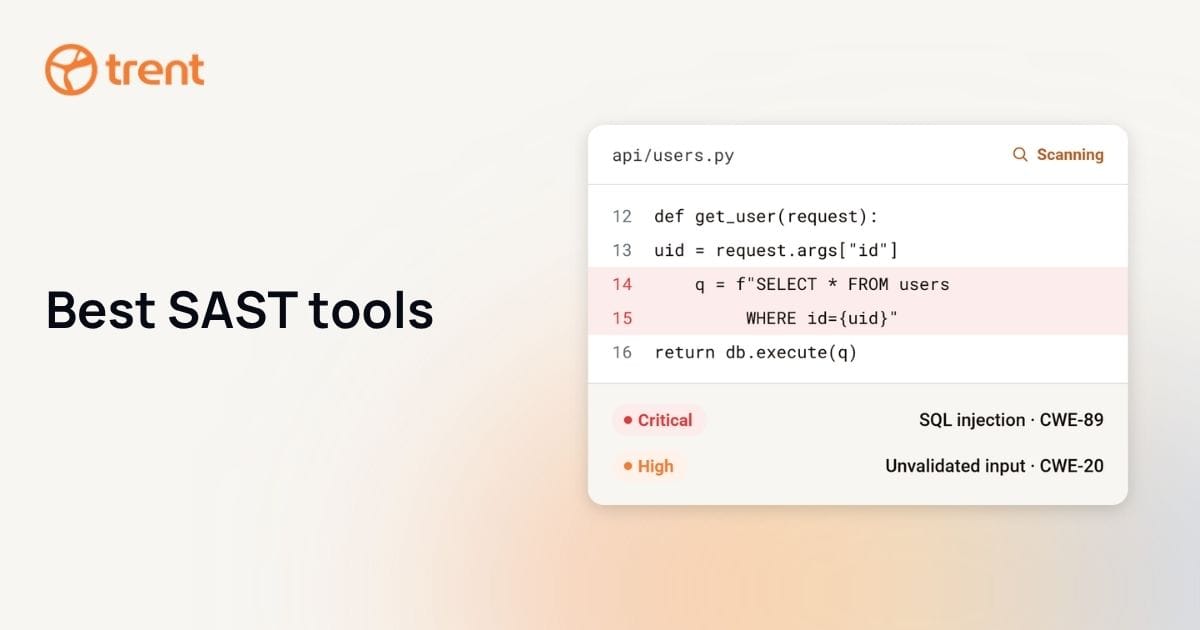
The 10 best SAST tools in 2026, from open source scanners to AI-native review, with pricing, licenses and features.
What the EU Cyber Resilience Act asks for in an SBOM, what DORA asks for in library tracking, and the continuous component inventory that answers both.
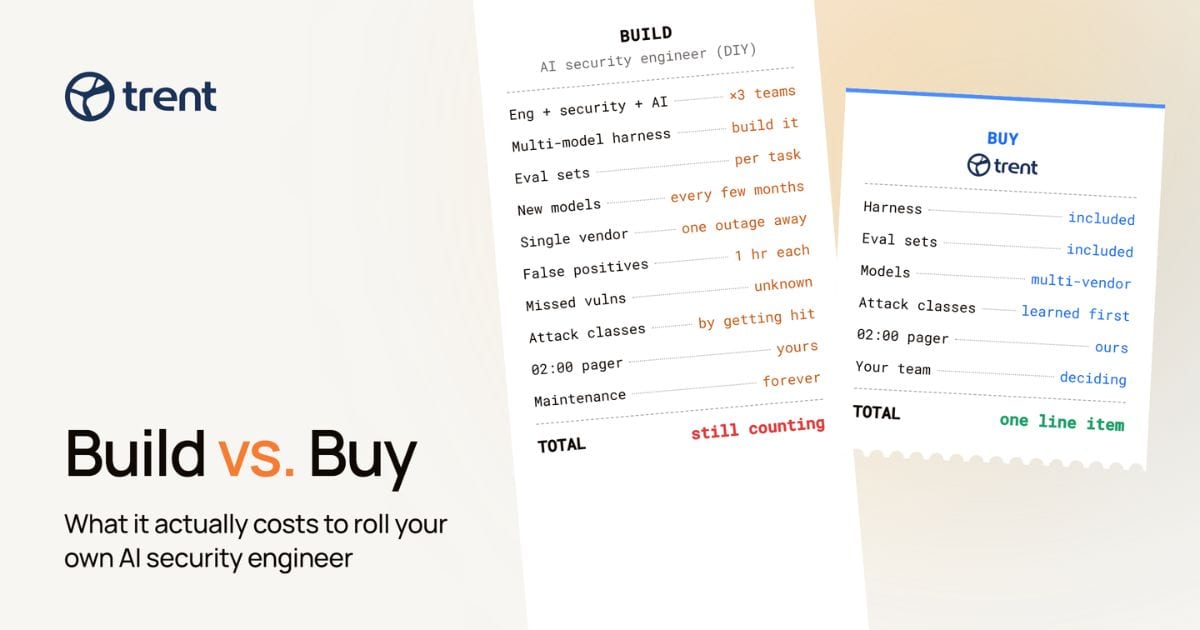
Can you build your own AI security engineer on a frontier model? What it really costs: misses, noise, vendor risk, new attack classes, and your best people.
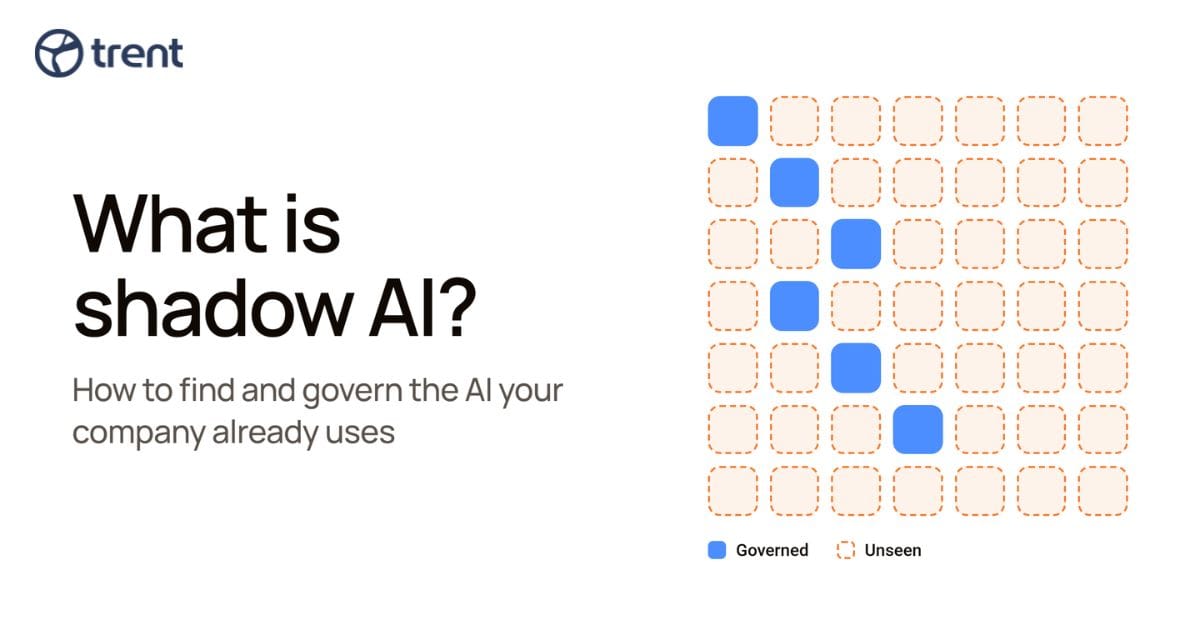
Shadow AI is AI your company uses without security approval. How to find it in apps and code, the risks ranked, a 30-day plan and a policy template.
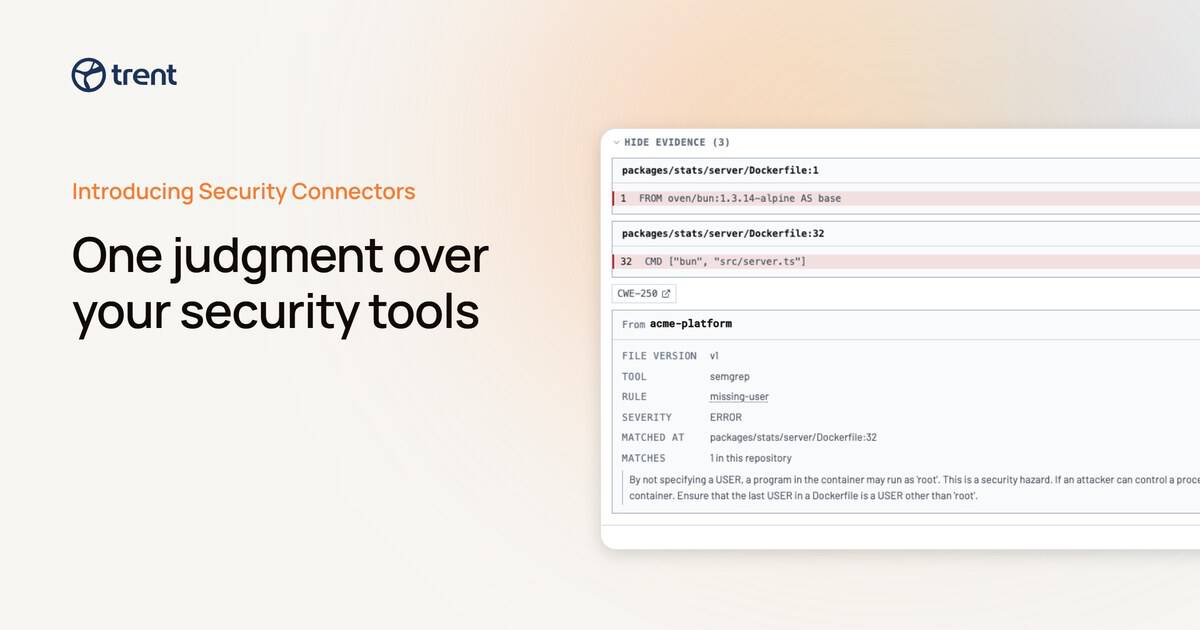
Trent now reads SARIF from any scanner and connects natively to Semgrep, then shows the exact evidence behind every finding and severity call.
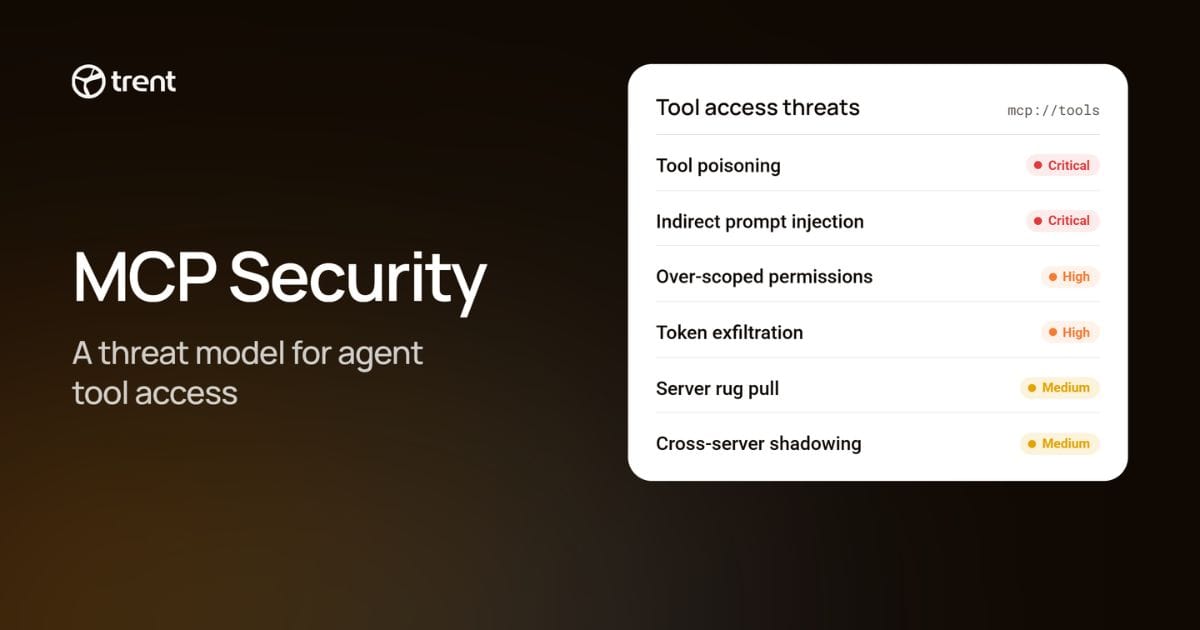
Connection auth is where MCP security starts, not ends. Tool poisoning, rug pulls, config secrets, and the local and remote split in Claude Code.
The EU Cyber Resilience Act for security teams: scope per product, classes, Annex I in engineering terms, both deadlines, and a build order to December 2027.
Most AI security maturity scores collapse the first time someone asks for proof. What evidence actually counts, and why an honest lower score wins.
What we use, build, and skip.
EU CRA reporting starts 11 Sept 2026. Use this engineering runbook for the 24-hour warning, 72-hour notification, and final report.
Trent AI Organization Workspaces give enterprise security, engineering, and product teams shared access to security analyses, findings, and remediation planning.
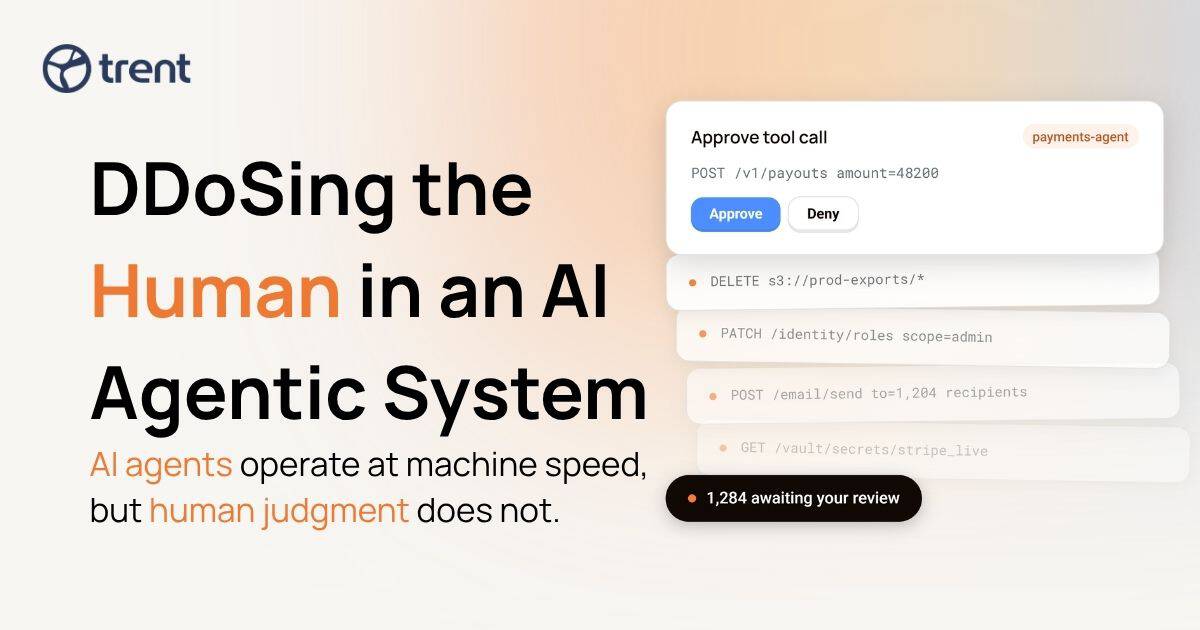
AI agents operate at machine speed, but human judgment does not. Explore the emerging risk of human DDoS attacks and how to protect the human layer.
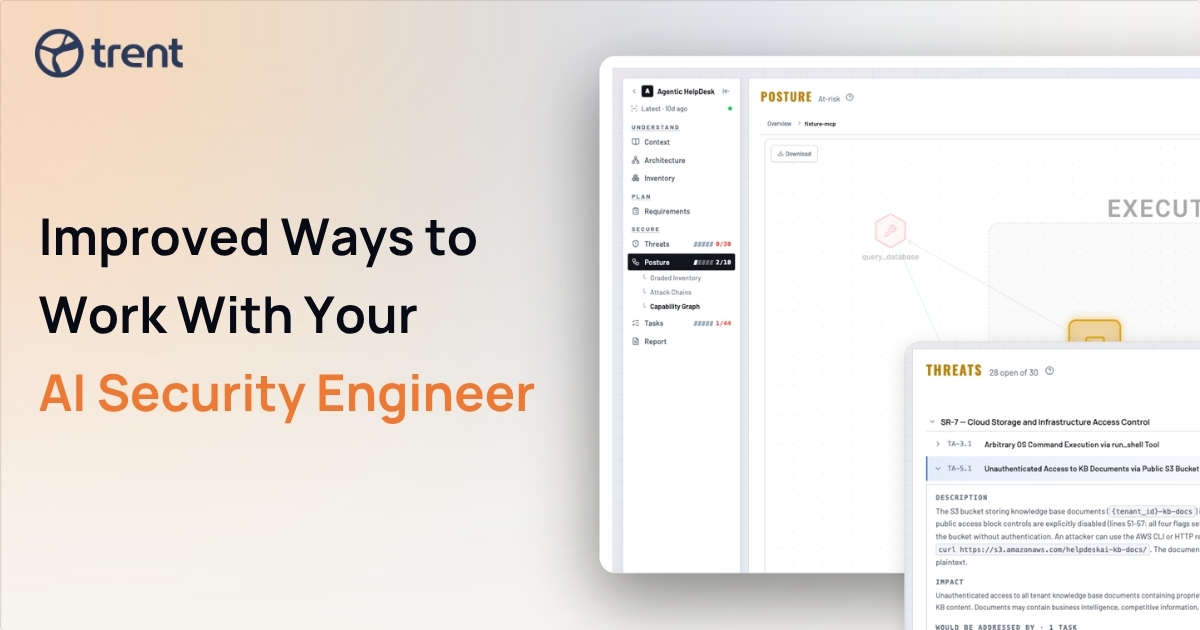
A new experience for Trent’s AI Security Engineer: one project from Understand to Plan to Secure, chat beside every page, and in-place regrades.
Compare STRIDE, ATT&CK, ATLAS, MAESTRO, SAILORS, PHANTOM-B and AGENTIC in 2026, and learn how to build a layered AI threat modeling strategy.
STRIDE, MAESTRO, and ATLAS all assume a human runs the threat model. Agentic software changes daily. The next step is threat modeling that AI agents can run.
The ASMM helps organizations assess AI security maturity, identify risks in agentic AI systems, and build a roadmap to secure AI-driven software development at scale.
See how Trent’s Security Program Mapper turns frameworks, security tools, and tech stacks into a defensible map of compliance coverage, control gaps, and priorities.
AI already knows how to solve hard problems. The missing ingredient is knowing when to act. Learn the information-judgment gap, and why defensive security is AI’s real frontier.
As AI agents become more autonomous, safety depends on preserving human judgment. Learn why the judgment layer is essential for secure agentic AI.
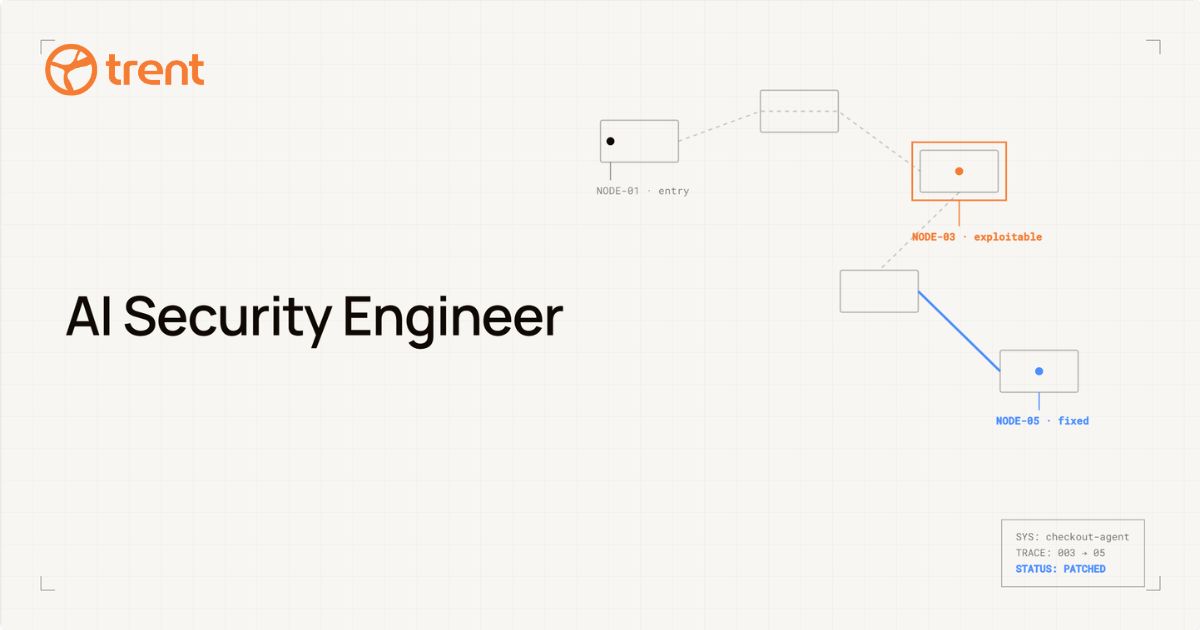
AI security engineer, defined: software built for agentic systems. It maps architecture, traces attack chains, and fixes what’s exploitable.
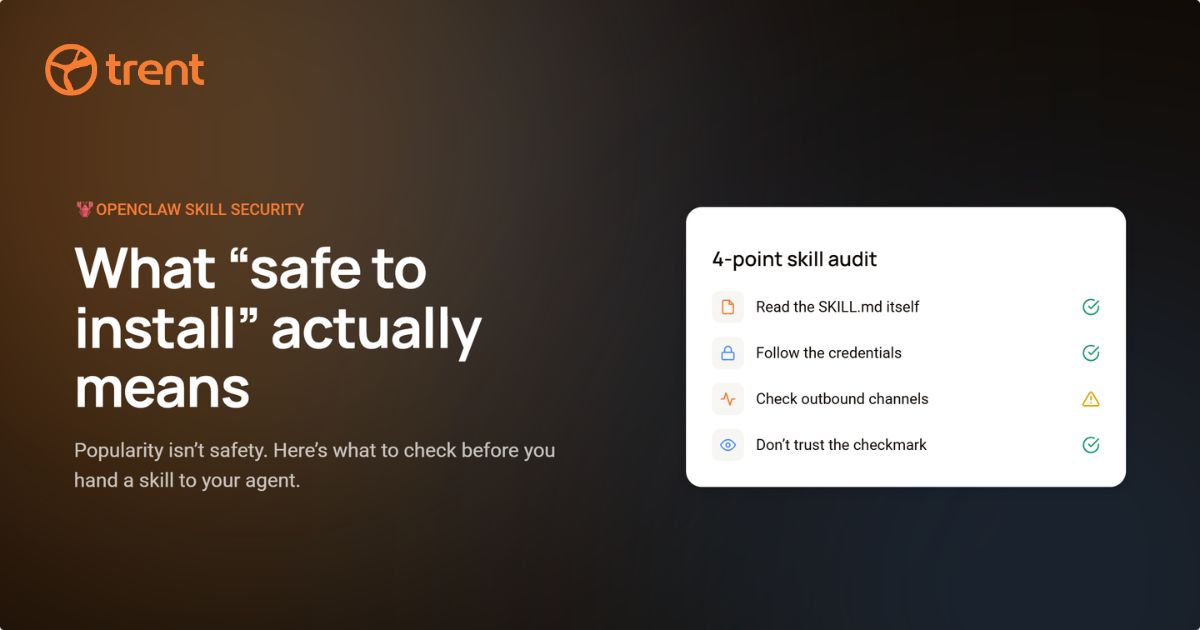
Every “best OpenClaw skills” list ranks by installs and stars. We pulled all 52,652 ClawHub registry packages: installs and stars tell you almost nothing about safety.
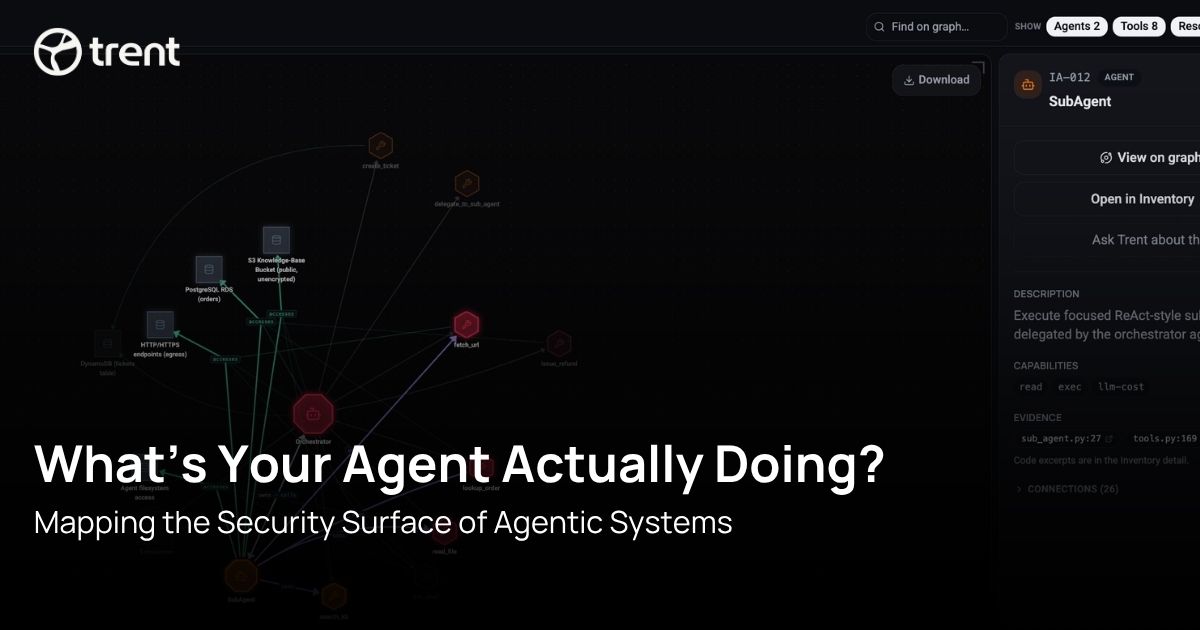
Map the security surface of agentic systems with Trent. Discover agents, tools, attack chains, data access, vulnerabilities, and prioritized fixes.
A working glossary of agentic AI security: opinionated definitions, from the AI security engineer to attack chains and failure modes.
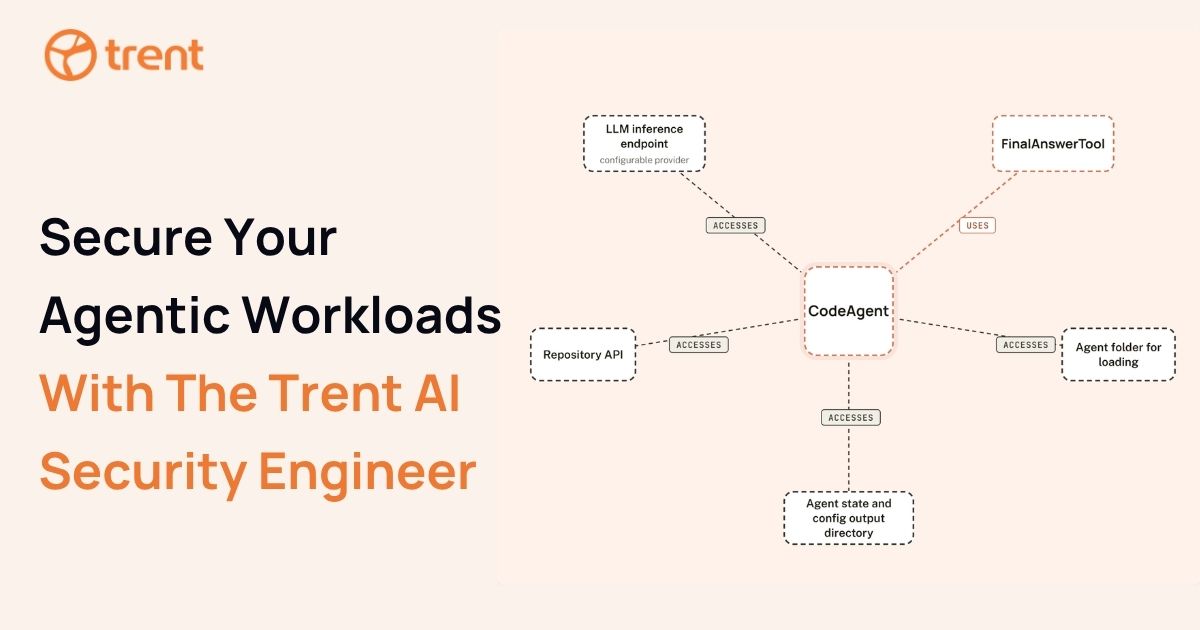
Meet the Trent AI Security Engineer for Agentic Workloads. Find attack chains, secure AI agents and CI/CD pipelines, and stop autonomous AI risks before deployment.
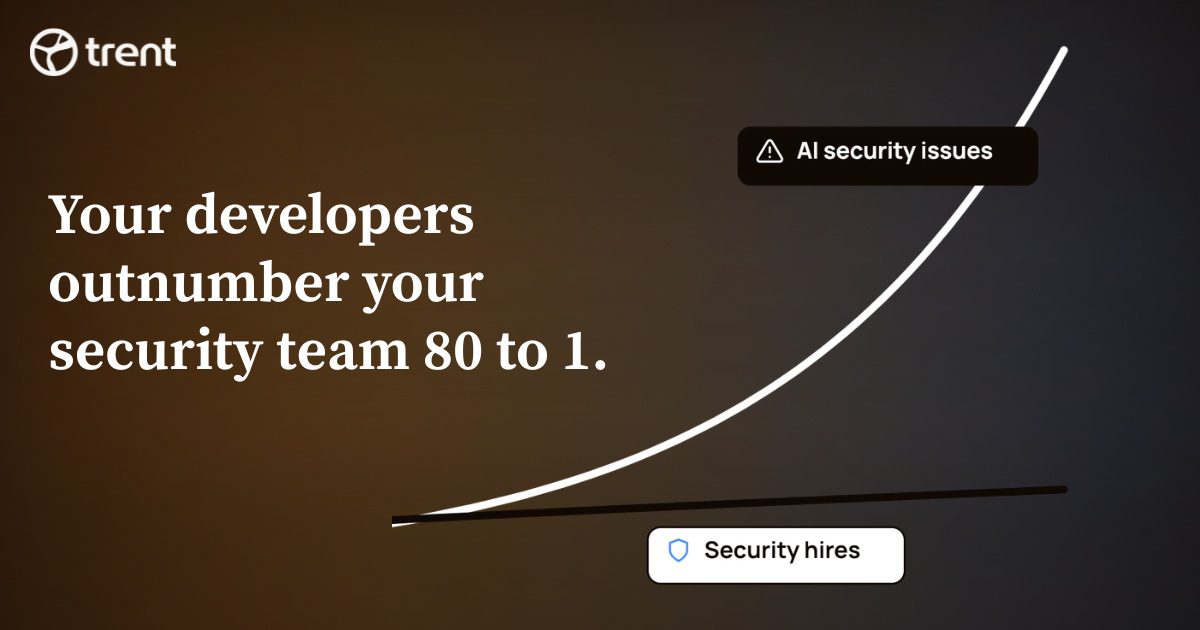
AI has fundamentally changed the economics of software security. As developer output accelerates, security teams can’t keep pace through hiring alone.
Install trentclaw and audit your OpenClaw setup in ~2 minutes: config, ClawHub skills, permissions, and custom code. Four steps, copy-paste commands.
OpenClaw security in four layers: 48 CVEs, a 0.0.0.0 gateway with no auth, 52,652 skills, and 86% of scanned packages vulnerable. The structural map the checklists miss.
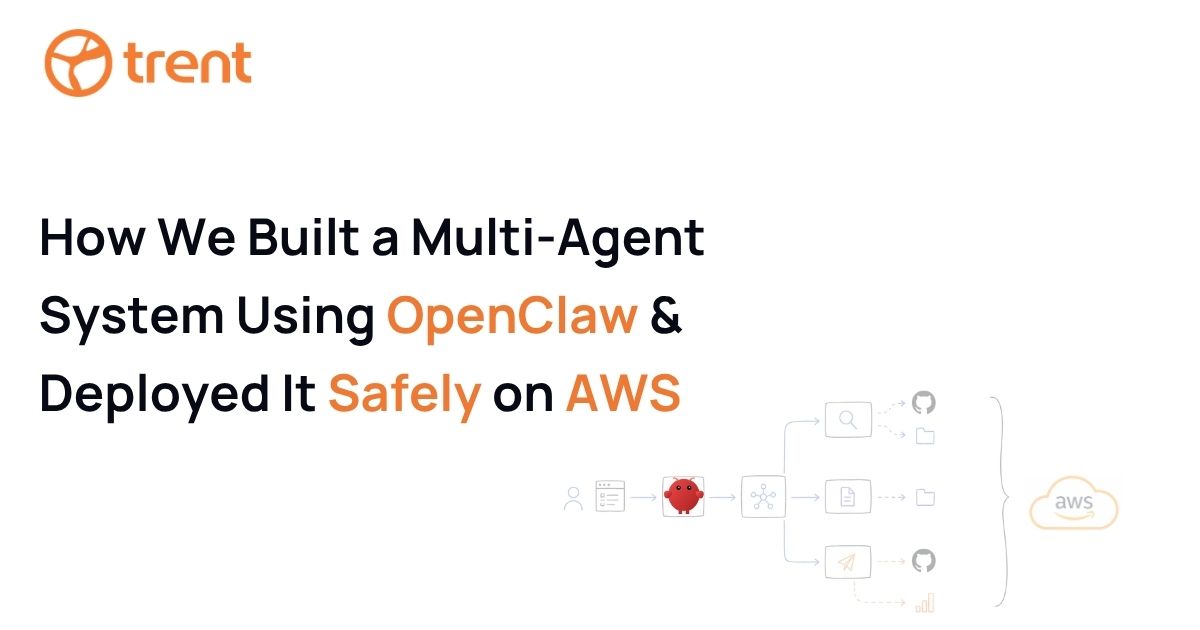
How we built a multi-agent code-to-doc pipeline on OpenClaw and ran it safely on AWS: least privilege, a tight blast radius, and agent containment.
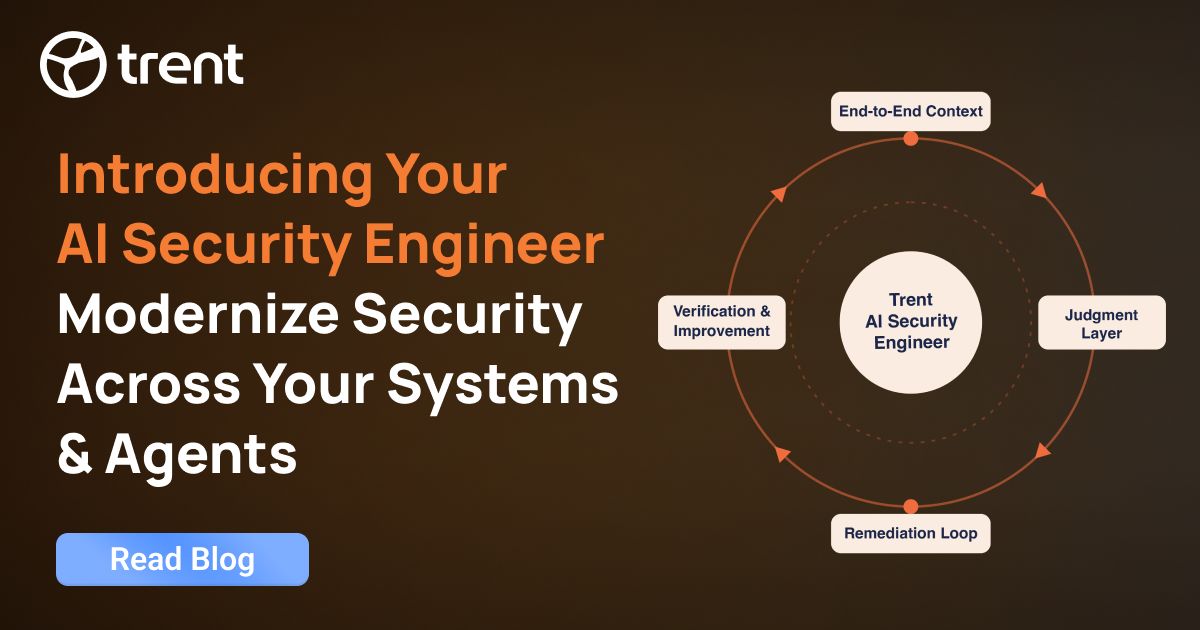
Meet Trent’s AI Security Engineer, a new way to modernize security across your applications, infrastructure, and AI agents with expert analysis, prioritized risks, and verified remediation.
See which of your OpenClaw skills are putting you at risk If you install skills on ClawHub: assume you are the auditor, because the registry isn’t doing it for you. openclaw skills install @trent-ai-release/trentclaw Install trentclaw →
We’re honored to announce that Trent has been named Agentic AI Security Platform Leader in the 2026 Cybersecurity Stars Awards by The Hacker News.
We pulled metadata on all 52,652 ClawHub packages. Only 22% are “clean”, one account published 1,941, and static scanning has nothing to scan.

It depends on your deployment. A practical security assessment of OpenClaw’s real risks and the controls that make it safe to run.
Three production lessons from building Trent’s MCP server: consolidate tools, keep naming consistent, and trust the schema, not just your tests.
Most RAG pipelines ship without a security model. Learn the threat taxonomy, OWASP LLM08:2025 risks, and how to secure each phase of your stack.
OWASP dropped the Top 10 for Agentic Applications. All ten ASI risks map back to entries in the LLM Top 10.
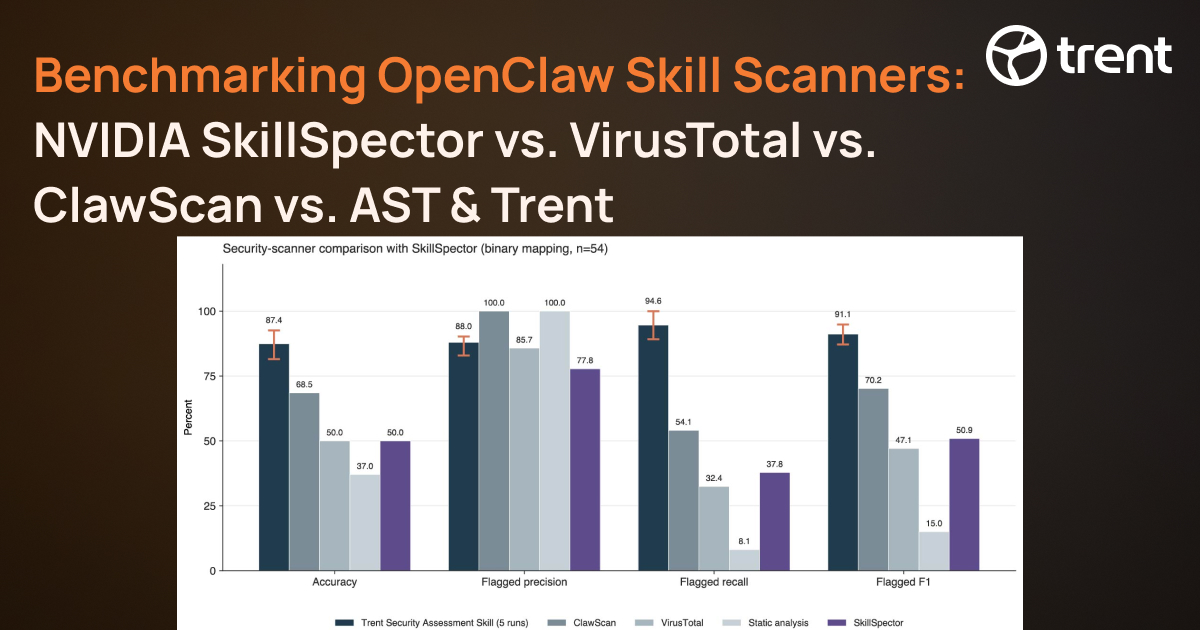
We benchmarked 5 security tools on 28 real CVEs from CWE-Bench: Semgrep, CodeQL, OpenAI Codex, Claude Code, and our own agent. The surprising result wasn’t the score. It was a gap inside the data.
You Can Ship within a Weekend. But Here’s How to Ship Securely.
Trent AI introduces ASMM, a framework to assess and improve enterprise security for agentic AI systems, aligned with NIST and global standards.
Trent’s Security Advisor for Claude Code, a security agent built specifically for providing ongoing security advice while building with Claude Code. Many of our customers and design partners tell us that building with Claude Code is incredibly powerful. It can generate secure code, develop implementation plans, and guide you through execution. And Claude Code (and … Trent AI Provides Continuous Security Advice for Claude Code Builders
A week of sessions, a designathon, and a lot of conversations about the impact of AI. Here’s what stuck with me and why it matters for how we design agentic systems. We kicked off CHI 2026 with a designathon meet-up; I helped co-organize: Generative Design and Vibe Coding: Rethinking The Design-Development Divide for UI Prototyping … Notes from CHI 2026: HCI, AI & the Future of Agentic Security
Our behavioral security analysis of 2,354 OpenClaw skills reveals why most packages are insecure by design, how prompt-injection supply chain attacks work, and what secure-by-default ecosystems need next.

From AI sovereignty to secure system design, this report from the India Summit examines why human judgment, governance, and engineering fundamentals matter more than ever.
Today, we’re excited to share that Trent AI has raised $13M in seed funding to build security for the agentic world. Our CEO shares the story behind why we started Trent.
Trent AI emerges from stealth with a unified agentic security platform and $13M in seed funding to help teams continuously scan, judge, mitigate, and evaluate risk across AI agents and autonomous systems.
Security shouldn’t start at launch. It should evolve with your product. Today we’re excited to introduce Trent’s Security Advisor for Lovable. An AI security agent purpose-built for Lovable builders shipping real products.
For the OpenClaw community, run an in-runtime security audit in minutes. Get severity-ranked risks (secrets, permissions, exposure) plus clear fixes.
LLM guardrails are runtime security controls protecting AI applications from prompt injection, data leakage, and unauthorized actions. OWASP mapping, AI firewall comparison, and decision framework.
Trent AI joins OWASP as a startup member to help secure agentic systems, applications, and workloads. Learn how we’re advancing protection against emerging AI threats.
Security is shifting from infrastructure control → autonomous system control. We’re living it every day at Trent AI, and so are the AI-native startups and enterprises we work with.
Threat modeling is a structured process for identifying and prioritizing potential security threats to a system, then defining countermeasures to prevent or mitigate those threats. It answers four key questions originally framed by Adam Shostack…
I work with an AI coding assistant daily. The striking thing is that it already “knows” everything it needs to get things right on the first try (debugging techniques, architectural patterns, security best practices) yet it can’t apply that knowledge reliably without my steering. That points to a deeper distinction between information and judgment, and it’s exactly the kind of gap reinforcement learning is meant to narrow.
STRIDE remains the most accessible gateway into systematic security thinking; and when extended thoughtfully, it continues to serve modern engineering teams more than 25 years after its creation.

Agentic AI systems can act, not just respond. Learn how to secure autonomous AI using STRIDE threat modeling, OWASP LLM guidance, and real-world attack scenarios.
What does Operations really look like at an early-stage AI startup? Trent AI’s Head of Operations shares lessons on building trust, lightweight structure, and scalable systems from day one.
A systems view on AI agents: how individual productivity gains create hidden costs, fragile workflows, and long-term organizational risk.
Artificial intelligence breakthroughs are increasingly coming from startups, not Big Tech, as AI lowers the cost of experimentation and innovation.
Trent AI is thrilled to announce that we have joined Carnegie Mellon University’s CyLab Venture Network as a Startup Partner.
How do you know when it’s time to start a new company? “I got a text saying, ‘Zhenwen and I quit our jobs. Things are getting real now’ and within a month we’d decided on our name,” said Neil Lawrence, Co-Founder and Chief Scientist at Trent AI.
Over the last year, I’ve found myself circling the same unease in different conversations, with different people, in different contexts. It comes up when talking about large language models, about agents, about productivity, and inevitably about security.
70% of security defects start in design, yet most teams still treat security as a pre-launch checklist. Here’s why the traditional approach is broken.
The interview question I asked 100+ candidates became reality: what happens when you’re the first security engineer at a startup with 3 months to launch?
Even AWS, with dedicated AppSec teams and deep pockets, struggles to scale secure software development. Here’s what that means for everyone else.
LLMs aren’t replacing infrastructure, they’re intensifying its use. Why the future of AI depends on architecture and security, not smarter models.
Excel broke on my iPhone the same week Big Tech admitted 30% of their code is AI-generated. Coincidence? Or a sign of something deeper.
Before you trust AI to secure your codebase, know this: today’s best models detect just 12.5% of real-world vulnerabilities without guidance.